Why a Read-Only Prompt Won't Protect Your SQL Server
TLDR;
Researcher Erik Hjelmvik reported CVE-2026-65669, a SQL Server elevation-of-privilege vulnerability that Microsoft rated critical. It involves Copilot in SQL Server Management Studio (SSMS). He presented the work at BlueHat Asia 2026 and published a write-up on September 30.
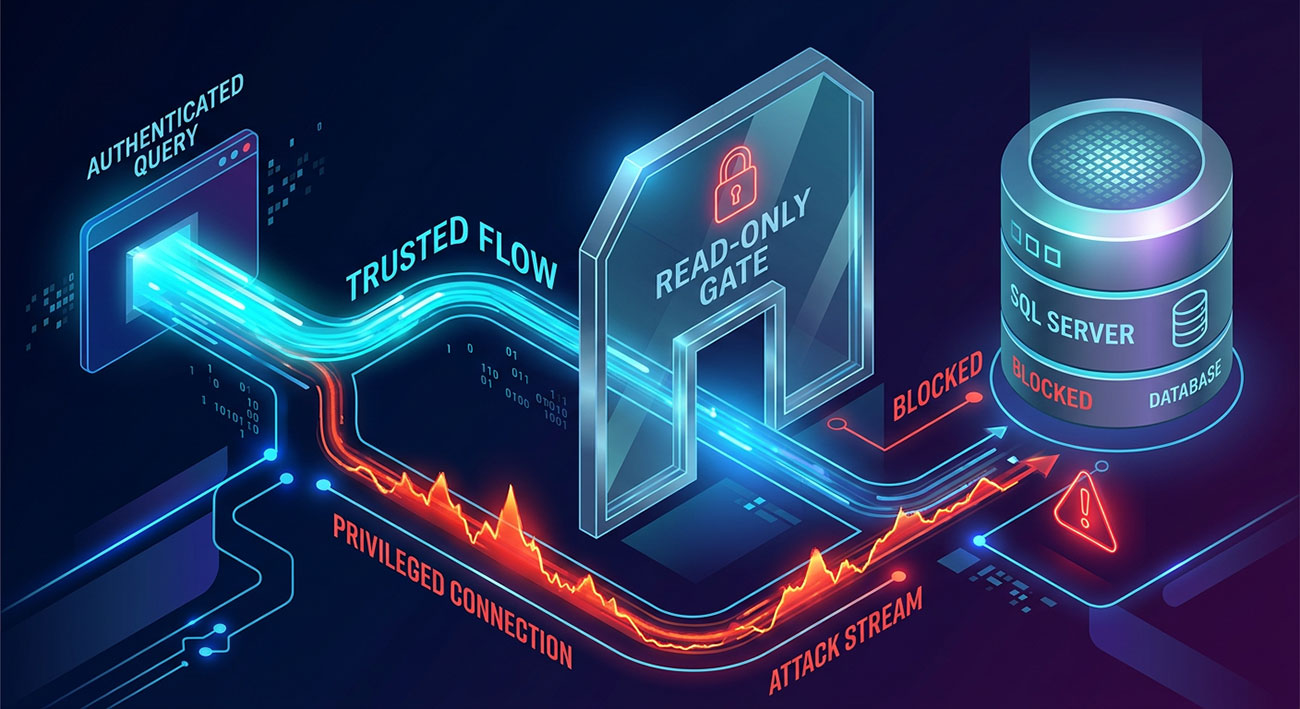
Copilot runs with the privileges of the connected user. Its “read-only” mode was a system-prompt instruction backed by a regex-based classifier, according to the write-up. There was no separate low-privilege connection or database permission enforcing read-only behavior.
A prompt can guide a database assistant. It cannot authorize one. Give it a separate, least-privilege identity.
What Actually Happened
Hjelmvik noticed that Copilot exposed only five tools until he opened an authenticated Query Window. After that, a much larger set appeared, including schema exploration, content reading, T-SQL validation, and backup operations.
The important detail: Copilot reuses the Query Window connection. Connect as sysadmin, and Copilot executes SQL as sysadmin.
The system prompt tells the model it is in read-only mode. By his account, the model refused obvious requests, such as invoking xp_dirtree. But a system prompt is not a security boundary. It is an instruction to software operating with the user’s real permissions.
Where Enforcement Lived
Hjelmvik reversed the code behind the ReadFromDatabase tool and found a regex-based classifier in a class called LocalSqlExecutionAccessChecker. One pattern, for example, blocked EXEC.
That is a weak place to put the control. SQL has too much syntax and too many edge cases for a pattern list to stand in for authorization. If the classifier misses a statement, that statement runs with whatever rights the connected user has.
Picture a DBA with a sysadmin session open who asks Copilot to inspect a slow report. Between that session and a damaging statement sit a polite model instruction and a list of regex patterns. Neither is the database saying, “This login cannot do that.”
I couldn’t see the full bypass details in the excerpt I was given, so I’m not going to describe how the classifier was beaten.
What to Check
If your team uses Copilot in SSMS, start with these questions:
- What SSMS build are you running? The researcher says to update, so confirm that you are on a patched version.
- Which login is active when people use Copilot? A sysadmin session is the worst case.
- Is Copilot configured with a separate execution context at all?
Ask the same question of every database assistant you run or buy: which credential actually executes its SQL?
What I’d Fix First
First, give the assistant its own identity. Microsoft’s admin documentation describes SSMS 22.7 or later letting administrators configure an agentExecuteAsUser in the database CONSTITUTION.md, so Copilot-generated queries run under a dedicated, least-privileged account. That’s the shape of the fix I’d want.
Then enforce read-only access in the database itself: SELECT on the schemas the assistant needs, no server-level object access, and no backup rights. The model can still be wrong, confused, or manipulated. The database should still refuse the operation.
If you do not need Agent mode, turn it off. The same documentation lists a Disable Agent Mode group policy for SSMS 22.7 and later. It also lists policies to disable Copilot for accounts or entirely from SSMS 22.4.1.
And keep admin sessions separate from Copilot. Opening a second window is cheap. Letting an assistant inherit sysadmin is not.
What Prompt Controls Can’t Do
A stricter system prompt will not solve this. Neither will a longer regex list. Both may prevent some accidents, which is useful. But they are safeguards around a component that can be steered; they do not change what the database credential is allowed to do.
Reviewing model refusals will not tell you enough either. The researcher saw sensible refusals while the real enforcement remained thin.
Final Thought
Authorization belongs where the data lives, enforced by something that cannot be talked out of it. A prompt can state intent. Only a permission can enforce it.
References and Further Reading
-
Embrace The Red — From SELECT to SYSADMIN with SQL Copilot (CVE-2026-65669) https://embracethered.com/blog/posts/2026/from-select-to-sysadmin-sql-copilot-bluehat-asia/
-
Microsoft Learn — Admin Controls - GitHub Copilot in SQL Server Management Studio https://learn.microsoft.com/en-us/ssms/github-copilot/admin-controls
-
wunderwuzzi23 on GitHub — SQL Copilot in SSMS system prompt, May 2026 https://github.com/wunderwuzzi23/scratch/blob/master/system_prompts/sql-copilot-in-ssms-may-2026.txt