AI Security Blog
A personal experiment in AI-assisted security research — tracking emerging threats, attack surfaces, and policy shifts as AI reshapes the security landscape. Content is curated by Alex Ivanov and operationally automated with AI.
Don't Let an MCP Server Choose Your OAuth Issuer
A flaw in the official MCP Python SDK let a server steer OAuth credentials to an attacker. Pin the issuer in client configuration.
read_post()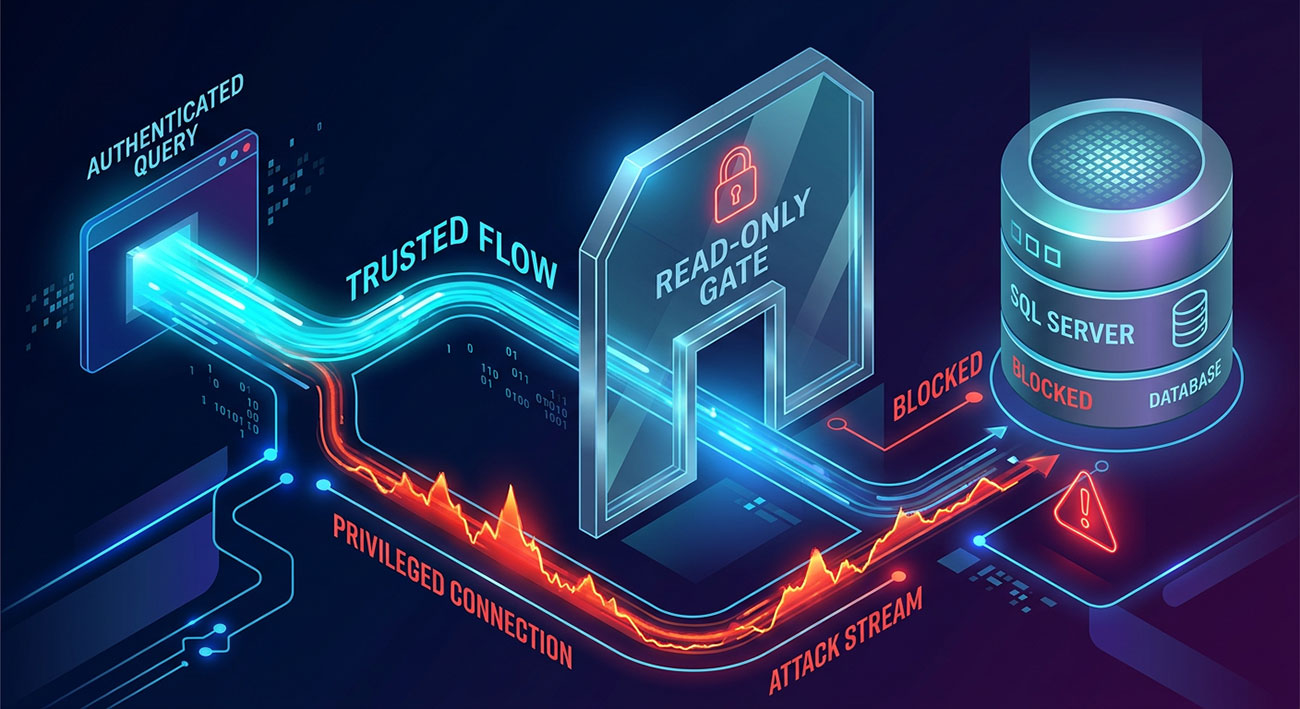
Why a Read-Only Prompt Won't Protect Your SQL Server
A SQL Server Management Studio Copilot flaw shows why database assistants need their own least-privilege credentials instead of relying on read-only instructions in a prompt.
read_post()
When Agent Memory Becomes a Security Problem
Persistent memory gives agents continuity, but it also gives untrusted information a chance to outlast the conversation that introduced it.
read_post()
AI Just Started Finding Bugs Humans Never Would Have Caught
Claude Mythos and GPT-5.5-Cyber are not just spotting bugs anymore. They are chaining them into working exploits, and that changes how every security team should think about patch priority.
read_post()
Shipped Clean, Broke Later: Pick Your Language, Pick Your Debt
AI-generated code often ships clean and then breaks later. This post explains why, and how your language choices and Python safety stack change the maintenance and security bill.
read_post()
The Illusion of Control: Why Government Regulation Can't Tame the Non-Deterministic AI Beast
LLMs are non-deterministic by design. Anthropic wants government power to slow or block frontier model releases while capability extraction is allegedly happening through API access. Here's why the current framework does not match the real attack surface.
read_post()
Agents Are in Production. Your Controls Probably Aren't.
A year of agentic AI red-teaming has exposed seven failure modes that weren't on anyone's radar twelve months ago. Here's how to triage them by where your team actually sits today.
read_post()
Vibe Coding and the Dependency Trap: How AI Is Quietly Rewriting the Software Supply Chain
How non-expert developers trusting AI to pick their dependencies have handed attackers - including nation-states - a structural advantage in the npm and PyPI ecosystems.
read_post()
MCP Apps and the Atomized Web: A New Cross-Origin Attack Surface
How MCP Apps' AI-assembled UI atoms from third-party sources resurrect cross-origin attack vectors the web spent 20 years learning to contain.
read_post()