Don't Let an MCP Server Choose Your OAuth Issuer
A flaw in the official MCP Python SDK let a server steer OAuth credentials to an attacker. Pin the issuer in client configuration.
Read postagentic-airesearch
Hands-on research, hardware, efficiency, and developer tooling.
A flaw in the official MCP Python SDK let a server steer OAuth credentials to an attacker. Pin the issuer in client configuration.
Read post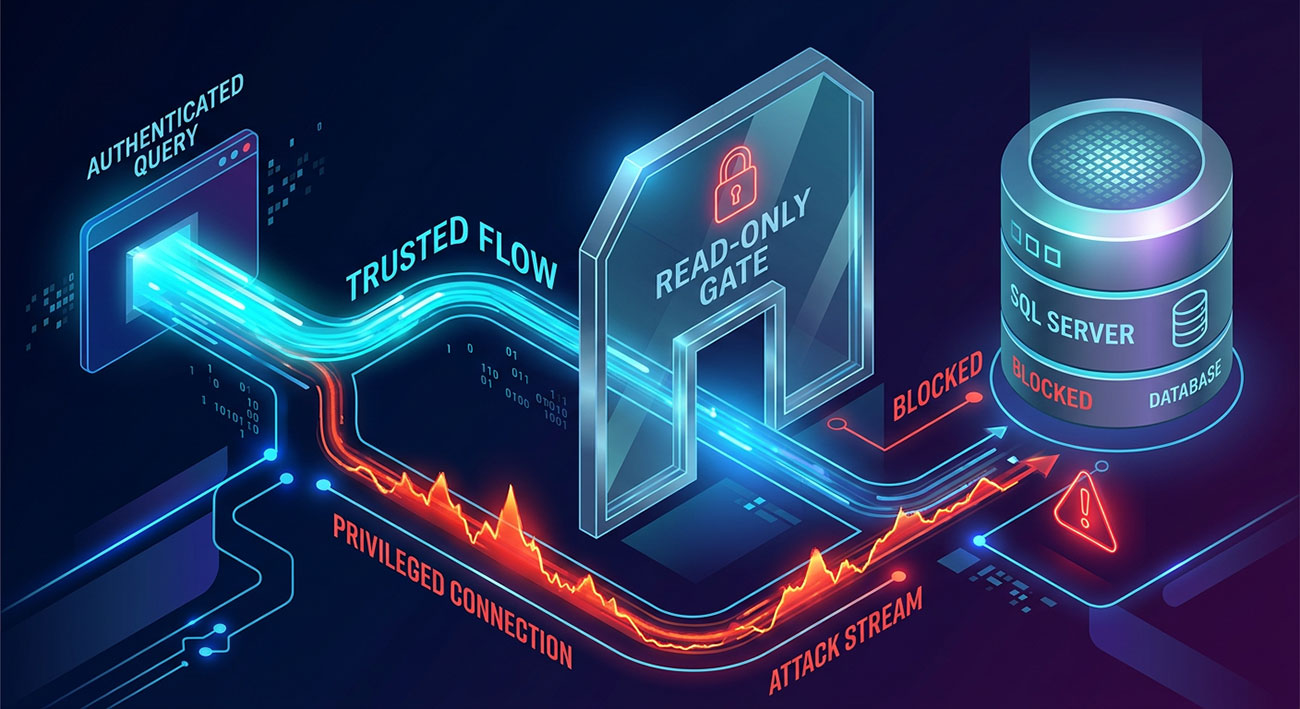
A SQL Server Management Studio Copilot flaw shows why database assistants need their own least-privilege credentials instead of relying on read-only instructions in a prompt.
Read post
Claude Mythos and GPT-5.5-Cyber are not just spotting bugs anymore. They are chaining them into working exploits, and that changes how every security team should think about patch priority.
Read post
A security‑first walkthrough for installing, hosting, and testing OpenClaw without handing it the keys to your life.
Read post
How secure sandbox environments are transforming AI engineering by making experimentation safer and security assessments sharper.
Read post
A comprehensive, modern list of verified developer tools dominating 2025 — featuring AI code agents, local model runners, vibe‑coding environments, advanced UI frameworks, and no‑code site builders — all linked directly to official vendors.
Read post
Explore how stochastic computing reduces AI operational costs and how AI security threats are evolving alongside advancements like Model Context Protocol (MCP). A comprehensive look at efficiency and protection.
Read post